What a CAA record controls
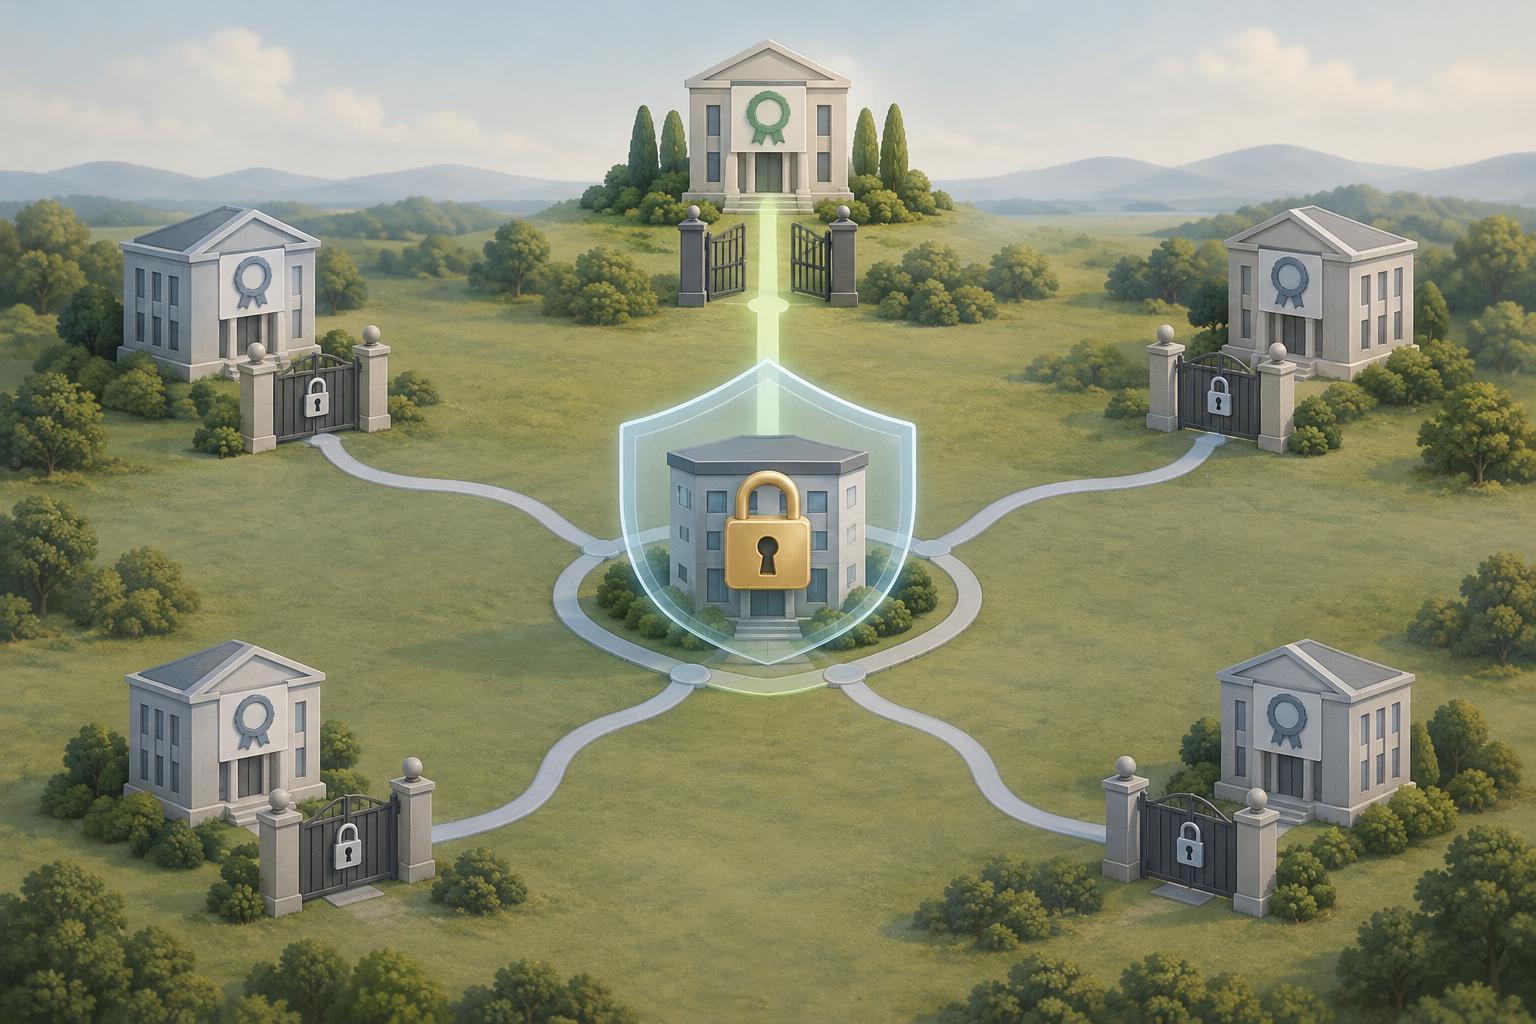
A Certificate Authority Authorization (CAA) record is a DNS record that tells certificate authorities which issuers you permit to create publicly trusted TLS certificates for a domain name. If you have no CAA policy, you have not used DNS to restrict the choice of issuer. Adding one can reduce the chance of a certificate being issued by an authority you did not intend to use.
CAA is a guardrail, not a replacement for domain security. It does not revoke certificates that already exist, prove that a website is safe, or protect access to your DNS account. A permitted authority must still validate a certificate request. Protecting your registrar and DNS provider accounts, and keeping track of who can change your DNS records, remain important.
Choose the right issuer permissions
A CAA record contains a flag, a tag, and a value. For example, 0 issue "ca.example" illustrates the format for allowing an issuer identified by ca.example. That issuer name is only a placeholder: before publishing a record, use the exact CAA identifier documented by the certificate authority you actually use. The flag is commonly 0 for these basic records.
The issue tag controls issuance of non-wildcard certificates. You can publish more than one issue record if more than one authority needs permission. The issuewild tag controls wildcard certificates, such as a certificate for *.example.com. If you set issuewild, treat it as a separate wildcard policy rather than assuming your issue records also allow wildcard issuance. A record with 0 issuewild ";" can be used to prohibit wildcard issuance at that name.
The optional iodef tag provides a contact destination for reports about CAA-related issuance problems, commonly as a mailto address. It is not a reliable alerting service on its own: whether you receive a report depends on the authority and the circumstances. Use an address you maintain, and remember that DNS records are public.
Put records where they will apply
A policy at example.com can apply to names beneath it, including www.example.com, unless a more specific CAA policy takes precedence. This makes the domain’s main DNS zone a useful starting point, but it also means a record added for a subdomain deserves careful review. Certificate authorities follow CAA lookup rules to find the applicable policy; checking only the exact hostname in a DNS tool may not show the full picture.
Before making changes, list the ways your organization obtains certificates. Include your web host, content delivery service, email service if it uses certificates for names under your domain, and any separate teams managing subdomains. A provider may issue or renew certificates automatically, so removing its issuer from CAA could interrupt a later renewal even while the current certificate continues to work.
Roll out and check a policy carefully
Start with the issuer identifiers required by the services you actually use. Add an issue record for each needed authority, then decide whether wildcard certificates should be allowed and, if so, which authority may issue them. You usually manage CAA alongside other DNS records in your DNS provider’s control panel. Follow that provider’s input format: some panels ask for the flag, tag, and value in separate fields, while others accept a single record value.
After saving, query the records, for example with dig CAA example.com. Check relevant subdomains too, and inspect any parent-domain policy that could apply to them. DNS changes may take time to appear through cached resolvers, so a single immediate lookup is not proof that every resolver sees the new policy. If available, compare the result from your DNS provider’s authoritative nameservers with a later lookup through an ordinary resolver.
Finally, verify that the service responsible for certificate renewal still lists an authorized issuer. Keep a small record of why each CAA entry exists and review it when you change hosting or certificate providers. A restrictive policy is most useful when it is accurate and maintained; an outdated one can block legitimate issuance without providing the protection you intended.