Two jobs behind a DNS answer
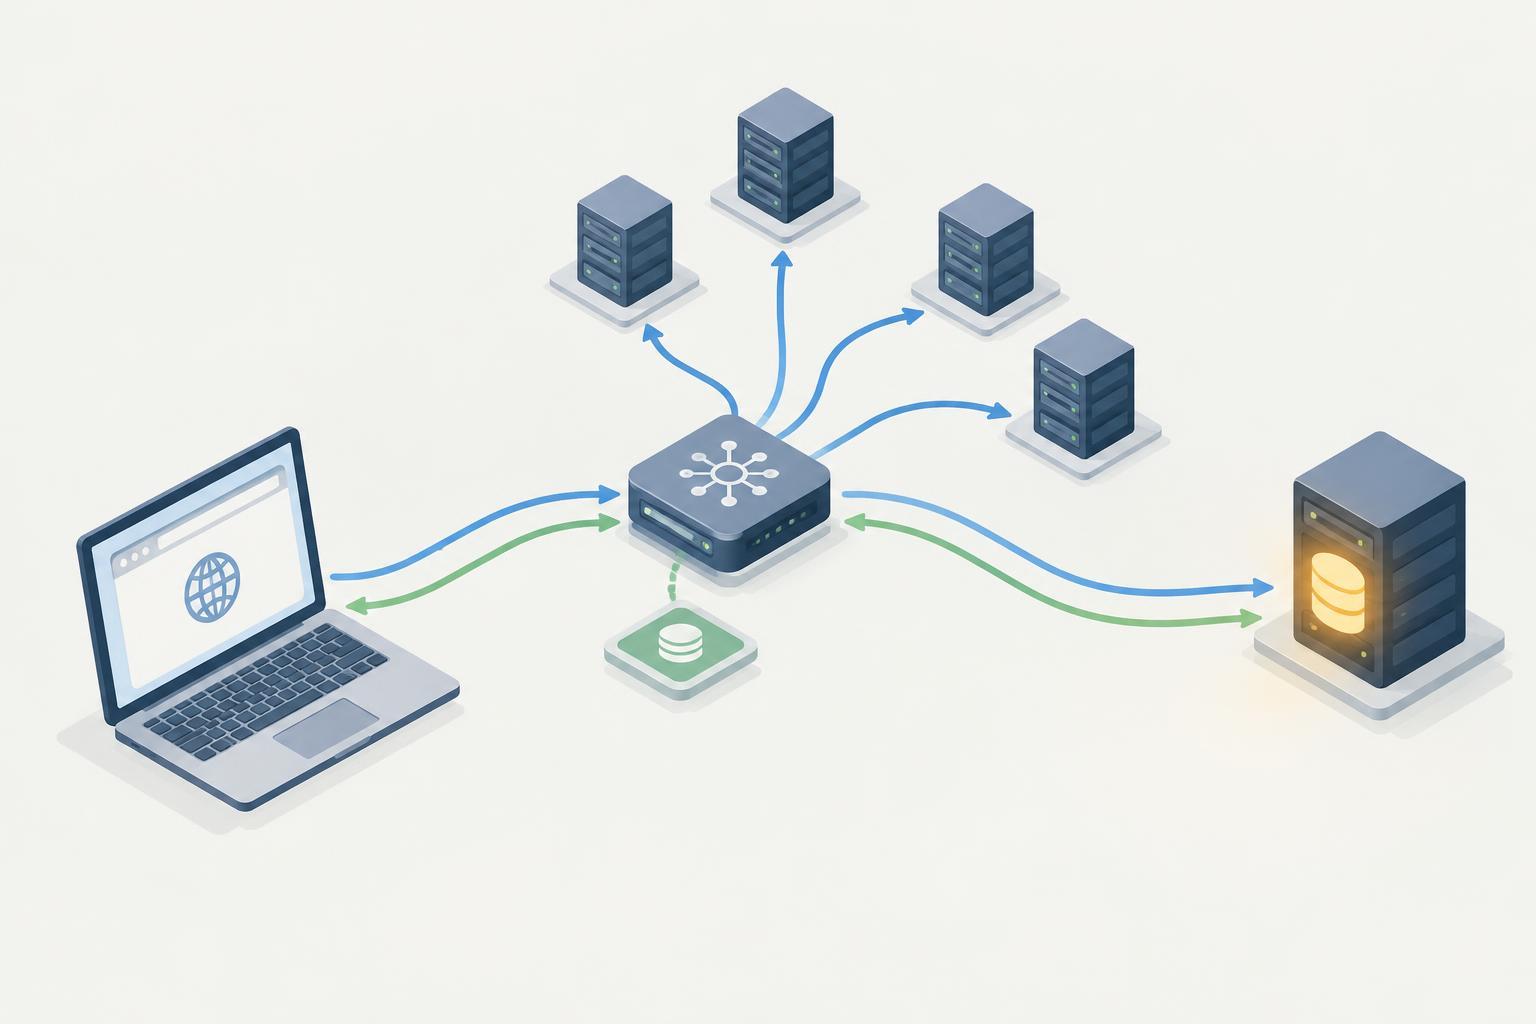
When you enter a website name, your device needs information that helps it connect to the right destination. DNS provides that information through records associated with domain names. Two kinds of servers have distinct roles in this process: a recursive resolver looks up an answer on behalf of your device, while an authoritative DNS server provides answers for a domain it serves.
Think of the recursive resolver as the server your device asks for help. It may already know the answer because it saved a recent result. If not, it works through the DNS hierarchy to find the appropriate authoritative server. That server does not browse the hierarchy on your device’s behalf; it responds with the records it holds for its portion of the domain namespace.
How a lookup reaches the authoritative server
Suppose an application asks for the address record of www.example.com. Your device typically sends the question to a configured recursive resolver. If the resolver has no usable cached answer, it can ask a root server where to find information for the .com top-level domain. The root server points it toward .com servers, which can point it toward the authoritative nameservers for example.com. The resolver then asks an appropriate authoritative server for the requested name and record type.
This sequence is often described as referrals: each level helps the resolver find the next place to ask. The authoritative server may return an address record, or it may return another relevant response, such as a CNAME pointing to a different name. If more lookup work is needed to obtain an address, the recursive resolver handles it before sending the result back to the device. The application can then use the answer to begin connecting; DNS itself does not deliver the web page.
What makes an answer authoritative
An authoritative server serves DNS data for a particular zone. A zone is the portion of the namespace managed together through DNS records. The domain’s delegation identifies which nameservers should be consulted for that zone. Depending on how a domain is organized, a subdomain may remain in the parent zone or be delegated to different authoritative nameservers.
Authoritative does not mean that a server has the final answer to every possible question about a domain. A name might not exist, or the name might exist without the requested record type. An authoritative server can give a definitive response about the data in its zone while still not providing the address record an application hoped to receive. By contrast, a recursive resolver generally returns information it obtained from authoritative servers or retained in its cache.
Why two people may see different answers
Recursive resolvers cache responses so they do not need to repeat the full lookup for every request. Records include a time to live, or TTL, that guides how long a resolver may keep a response. DNS can also cache certain negative answers, such as a response indicating that a name does not exist. Local device or application caches may add another layer between you and the recursive resolver.
After a record changes, one resolver may have the new answer while another still holds an earlier cached response. That difference does not necessarily mean the authoritative servers disagree. It may reflect when each resolver last looked up the name and how long its cached response remains valid. Checking both the authoritative answer and the answer from the resolver your device uses helps distinguish a record-setting problem from a caching delay.
A practical way to troubleshoot
Start with the exact name and record type you expect, such as an A record for www.example.com or an MX record for example.com. Confirm that the domain is delegated to the intended authoritative nameservers, then check what those servers answer. If they do not return the expected record, review the records in the relevant zone and whether a subdomain has been delegated elsewhere.
If the authoritative answer is correct but your usual recursive resolver gives an older result, compare the answers again after the cached response has had time to expire. Keep in mind that a successful DNS lookup only establishes that DNS returned an answer. If the website or mail service still does not work, the next issue may be elsewhere, such as the destination server, its configuration, or the network path.


