Two protections for two different questions
When you enter a domain name, your device usually asks a recursive resolver to find the records needed to reach a website or service. Two security questions arise: Is the answer the one the domain owner published? And can someone watching the connection between your device and the resolver read the question? DNSSEC addresses the first question. Encrypted DNS addresses the second.
These protections are complementary, not competing alternatives. A DNSSEC-validated answer can still have been requested over an unencrypted connection. An encrypted query can still receive an incorrect answer if the resolver does not validate it or the domain is not protected by DNSSEC. Neither technology, by itself, establishes that a website is trustworthy or that your entire browsing session is private.
What DNSSEC verifies
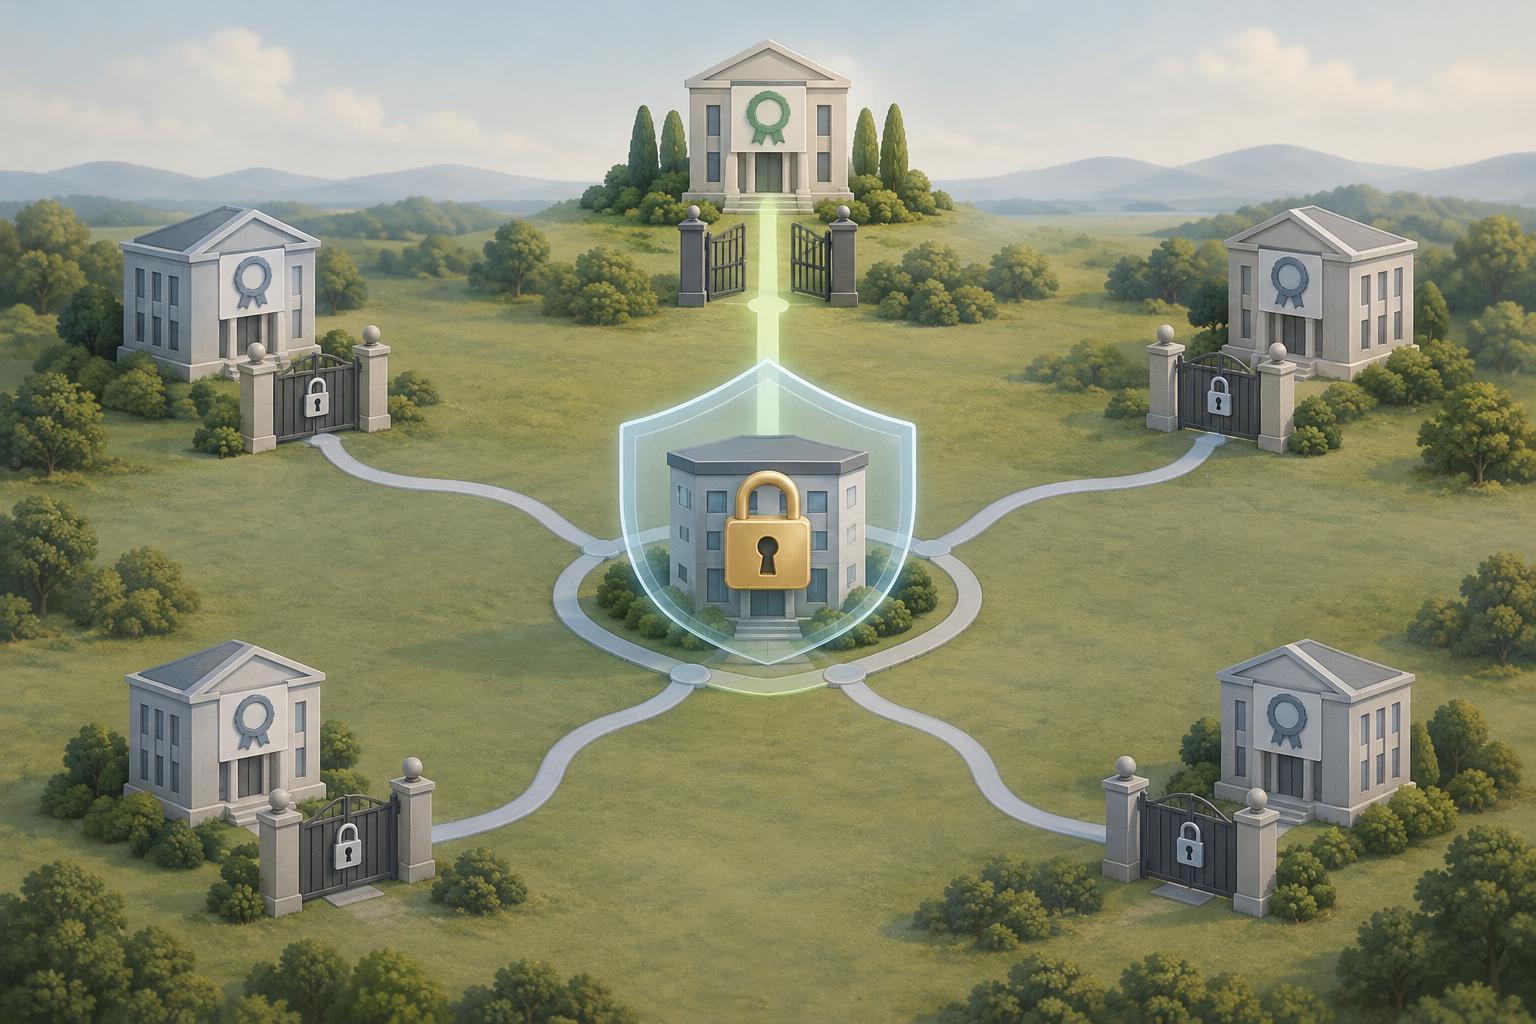
DNS Security Extensions, or DNSSEC, add digital signatures to DNS data. A validating resolver uses those signatures to check whether an answer is consistent with the signed records published for a domain. The checks depend on a chain of trust: a signed parent zone points to the child zone’s signing key through a DS record, and the resolver checks the relevant DNSKEY and signature records. When that chain is intact, an attacker cannot simply substitute a different DNS answer and make it pass validation.
DNSSEC can also provide signed proof that a requested record does not exist. It does not encrypt a query or hide the answer. It confirms DNS data against a chain of trusted keys; it does not confirm the intent of the person who registered the domain. A convincing imitation domain can have correctly signed DNS records of its own.
A missing signature is not always a validation failure. A domain that has not enabled DNSSEC may be treated as unsigned, while a signed domain with a broken chain or invalid signatures may be treated as bogus. A validating resolver will generally refuse to return bogus data, which protects users but can make a misconfigured domain appear unreachable.
What encrypted DNS protects
Encrypted DNS protects the connection used to send DNS queries, commonly between a device and its chosen recursive resolver. DNS over TLS (DoT) and DNS over HTTPS (DoH) are two ways to carry those queries over encrypted connections. Someone observing that stretch of the network, such as an operator of a shared Wi-Fi network, cannot read the DNS question from that encrypted traffic in the way they could read a conventional plaintext DNS query.
The resolver still needs to process the question and can see what it receives. Depending on how resolution is handled, other DNS servers may also see portions of the lookup. Encrypted DNS is therefore not end-to-end secrecy between your device and the domain you visit. Connections to websites can reveal information through other means, so encrypted DNS should not be treated as an anonymity tool.
A setting labeled “secure DNS” may refer to an encrypted transport, DNSSEC validation, or both. Check what a product actually enables rather than relying on the label. In particular, choosing a DoH or DoT resolver does not automatically mean it validates DNSSEC.
How they work together in a lookup
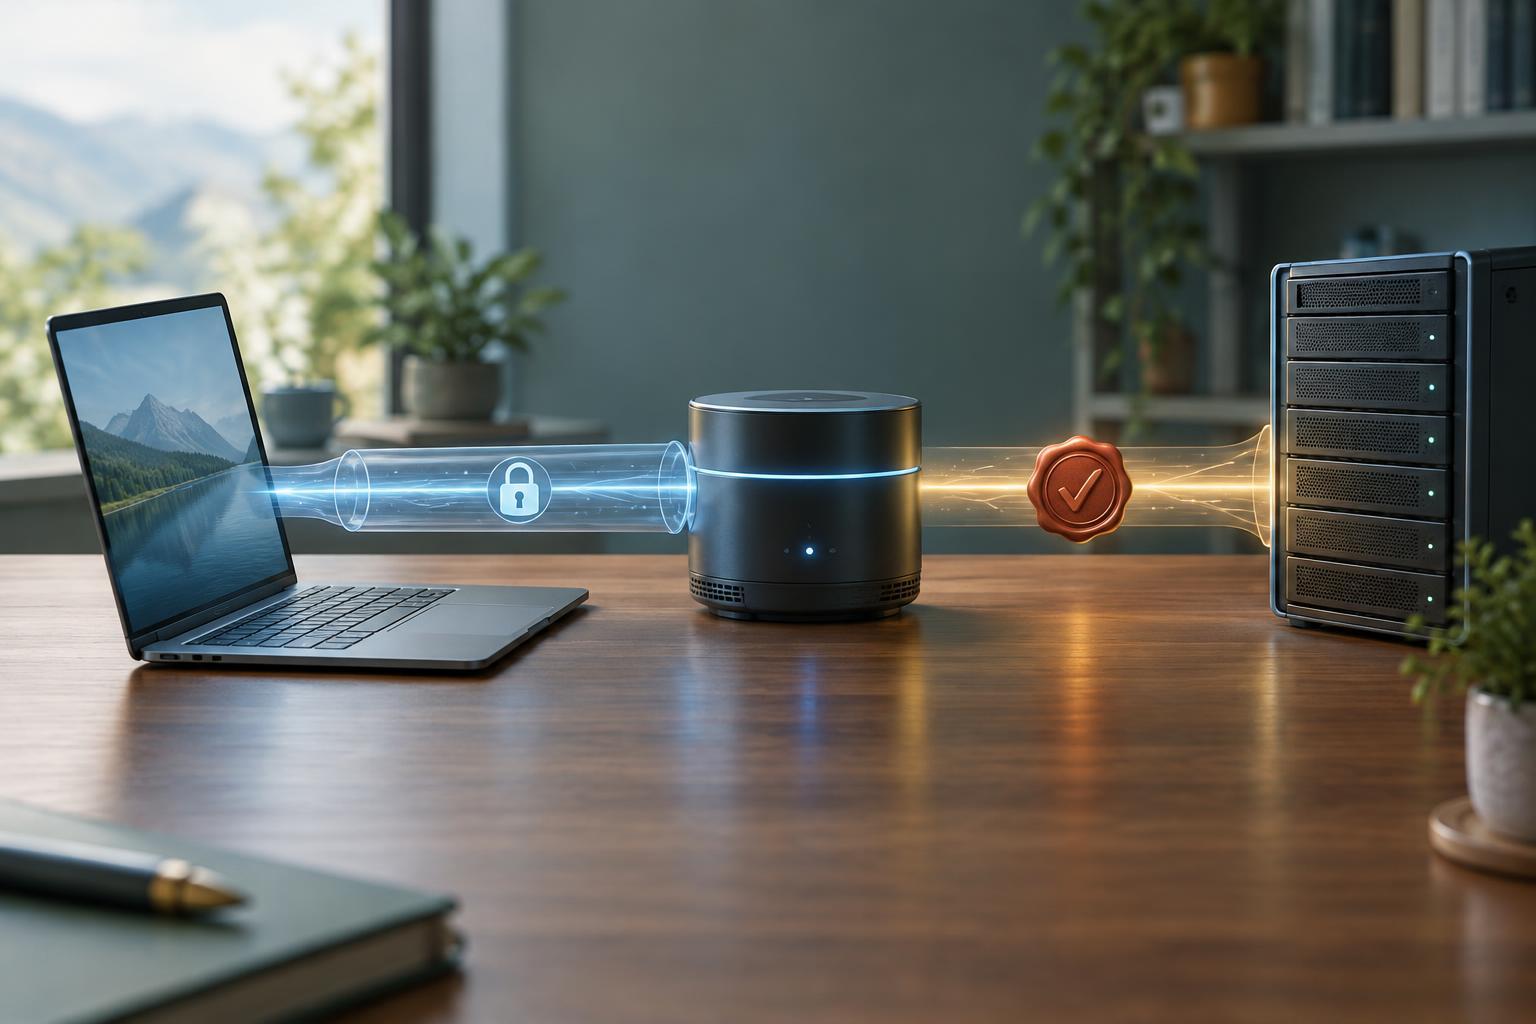
Imagine looking up the address for a domain. With DoH or DoT enabled, your device sends the question to a resolver over an encrypted connection. If that resolver validates DNSSEC and the domain has a working chain of trust, the resolver also checks the signed DNS answer before returning it. The encrypted connection protects the device-to-resolver exchange; DNSSEC helps protect the integrity of the answer the resolver accepts.
The distinction matters when troubleshooting. If encrypted DNS cannot connect, check the device’s resolver settings and whether the chosen service is reachable. If DNSSEC validation fails, investigate the domain’s signatures, keys and parent-zone DS record. Switching to an unencrypted resolver will not repair a broken trust chain; switching off validation may make the name resolve but removes the check that exposed the problem.
Practical choices for domain owners and users
If you manage a domain, enable DNSSEC only with a clear understanding of how your DNS provider handles signing and key changes. Confirm that the DS record at your registrar matches the active signing setup. When changing DNS providers, plan the DNSSEC transition carefully: stale DS records can cause validating resolvers to reject an otherwise available site or mail domain. Keep account credentials and signing keys out of support tickets and public troubleshooting examples.
If you are choosing a resolver, look separately for encrypted DNS support and DNSSEC validation. Use settings you understand, and be aware that a network or device may use a different resolver than the one you expected. For a simple mental model, remember: DNSSEC helps answer “Can this DNS data be verified?” Encrypted DNS helps answer “Who can read my query on the way to my resolver?” Using both addresses more of the lookup’s risks, while leaving other website and account security needs in place.