What the three checks actually measure
SPF, DKIM, and DMARC answer related but different questions. SPF checks whether the server delivering a message is authorized by the domain used in its SMTP envelope sender address. That address is used during delivery and may differ from the From address a reader sees. DKIM checks a cryptographic signature covering selected message headers and the body. The signature identifies a signing domain, which may also differ from the visible From domain.
DMARC connects those checks to the visible From address. A message passes DMARC when either SPF passes with an aligned envelope sender domain or DKIM passes with an aligned signing domain. Alignment means the relevant domain matches the visible From domain under the domain’s DMARC settings. SPF or DKIM can therefore pass on its own while DMARC fails.
For a message sent directly from an organization’s mail service, those identities can be arranged to work together. Forwarding and mailing lists add another system between sender and recipient. That system may change the delivery path, the message content, or both.
Why forwarding often breaks SPF
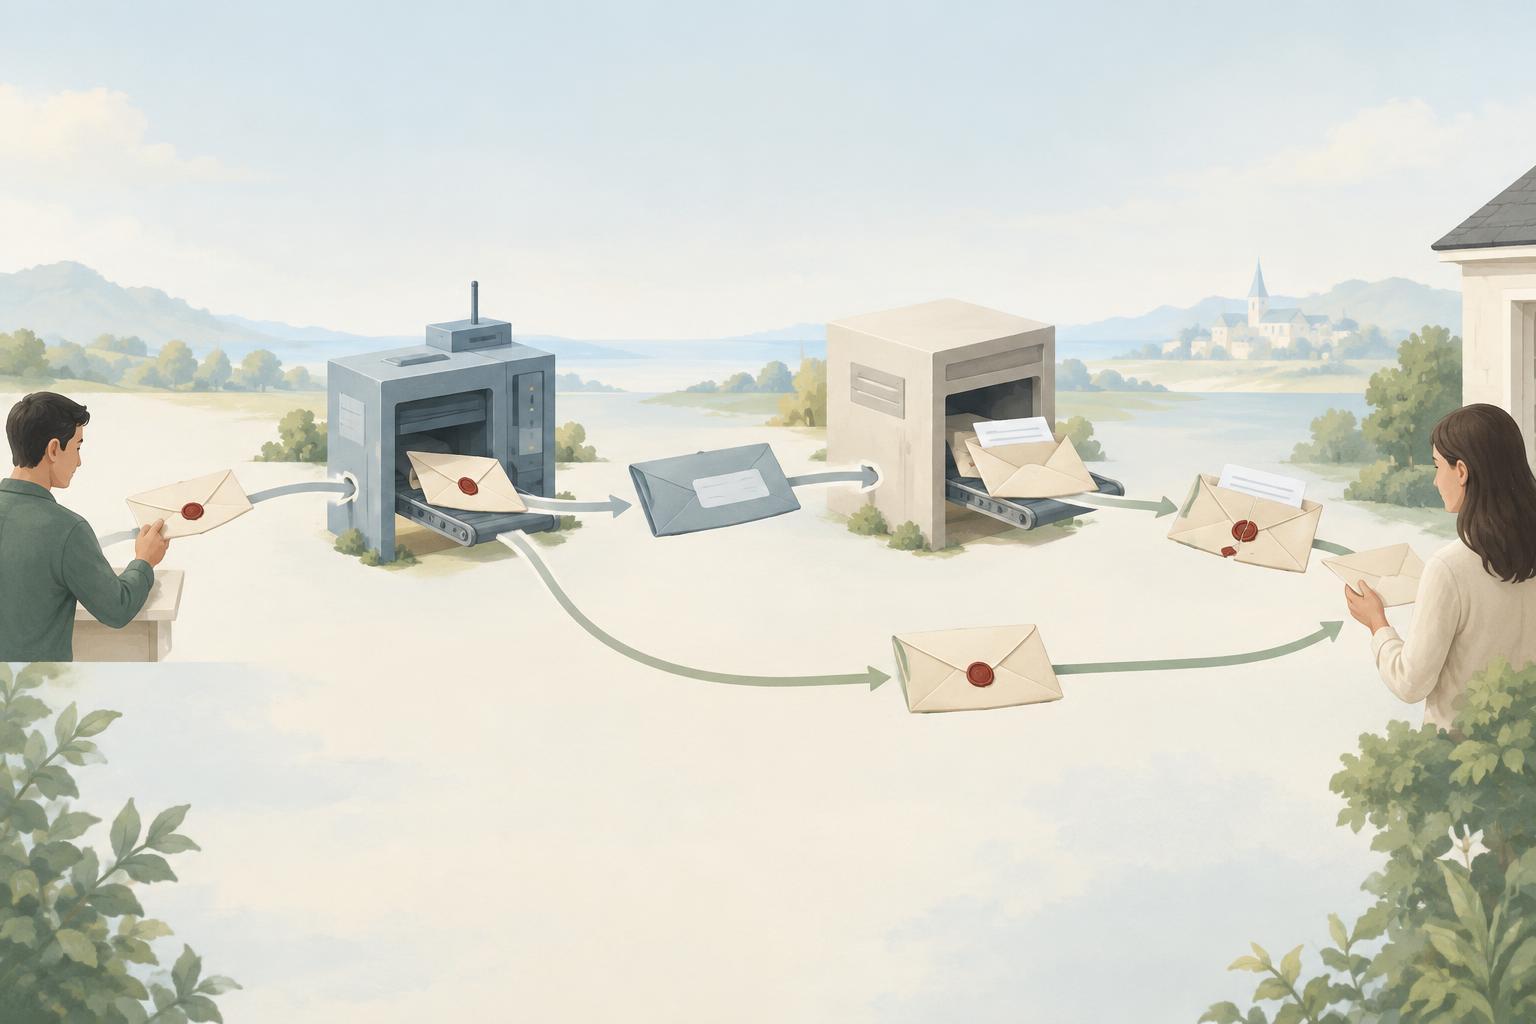
Suppose a sender at example.com emails an address that forwards all incoming mail to a second mailbox. The final mailbox receives the message from the forwarding server, not directly from example.com’s sending server. If the original envelope sender remains in place, the final receiver may check that forwarding server against example.com’s SPF record. Because example.com does not usually authorize an unrelated forwarder to send its mail, SPF may fail. This does not, by itself, prove that the message was forged.
Some forwarding services use Sender Rewriting Scheme, or SRS, to replace the envelope sender with an address under a domain they control. That can allow SPF to pass for the forwarding service’s domain and helps route delivery errors back through the forwarder. It does not necessarily make SPF pass DMARC: the rewritten envelope sender may no longer align with the original visible From address.
If the original message has a valid, aligned DKIM signature and the forwarder leaves the signed parts intact, DKIM may still pass and satisfy DMARC. Forwarding is consequently more reliable for authentication when the original sender signs mail correctly, but it is not guaranteed to preserve every signature.
Why mailing lists create another set of changes
A mailing list receives a message and redistributes it to subscribers. Like a forwarder, it becomes the server that delivers mail to the final recipient, so SPF for the original sender may fail. A list may also add a subject prefix, footer, or unsubscribe text. Changes to signed content can invalidate the original sender’s DKIM signature, leaving neither SPF nor DKIM able to pass DMARC for the original visible From domain.
A list operator may address this by replacing the visible From address with an address at the list’s domain and signing the redistributed message with that domain. This can produce aligned authentication for the list’s message, but it changes what subscribers see as the sender and may affect how replies work. Another list might avoid modifying message content to preserve the original signature, although its features and delivery behavior may then differ.
Adding a mailing list’s servers to every member’s SPF record is generally not a sound fix. A subscriber’s SPF record describes servers authorized to send using that subscriber’s envelope domain; list redistribution and DMARC alignment need to be considered separately.
How to investigate an unexpected failure
Start by identifying the route. Was the message delivered directly, forwarded from another mailbox, or redistributed by a list? In the receiving mailbox’s message details, look for the authentication results reported by that receiving service. Compare the visible From domain with the SPF envelope domain and the domain in any DKIM signature. A result such as “SPF pass” is not enough on its own: check whether that passing domain aligns with the visible From domain and whether DMARC passed.
If DKIM failed, compare an original copy with the forwarded or list-delivered copy where possible. A changed footer or subject may explain the failure, though message details alone may not identify every alteration. For a domain you manage, verify that your legitimate sending services use the intended SPF configuration and aligned DKIM signing. Keep test messages free of passwords, account recovery links, and other sensitive content when sharing them for troubleshooting.
Choose fixes based on who controls each hop
A sender can configure its own outgoing mail to authenticate with aligned DKIM and SPF, but it cannot control every forwarder or mailing list a recipient uses. A forwarding operator can consider SRS and avoid altering signed content. A list operator can assess whether preserving original signatures or using a list-domain From address better fits its service. Each choice has tradeoffs; no single DNS record repairs every intermediate change.
Some intermediaries add Authenticated Received Chain, or ARC, information to describe authentication observed before forwarding. A receiving service may use that information when deciding how to handle a message, but ARC does not itself turn a failed DMARC result into a pass or guarantee delivery.
Before changing a domain’s DMARC policy in response to delivery complaints, identify which mail flows fail and why. Loosening a policy may allow unwanted mail as well as legitimate forwarded mail. Understanding the route and the domain identities at each step usually points to a more precise remedy.


