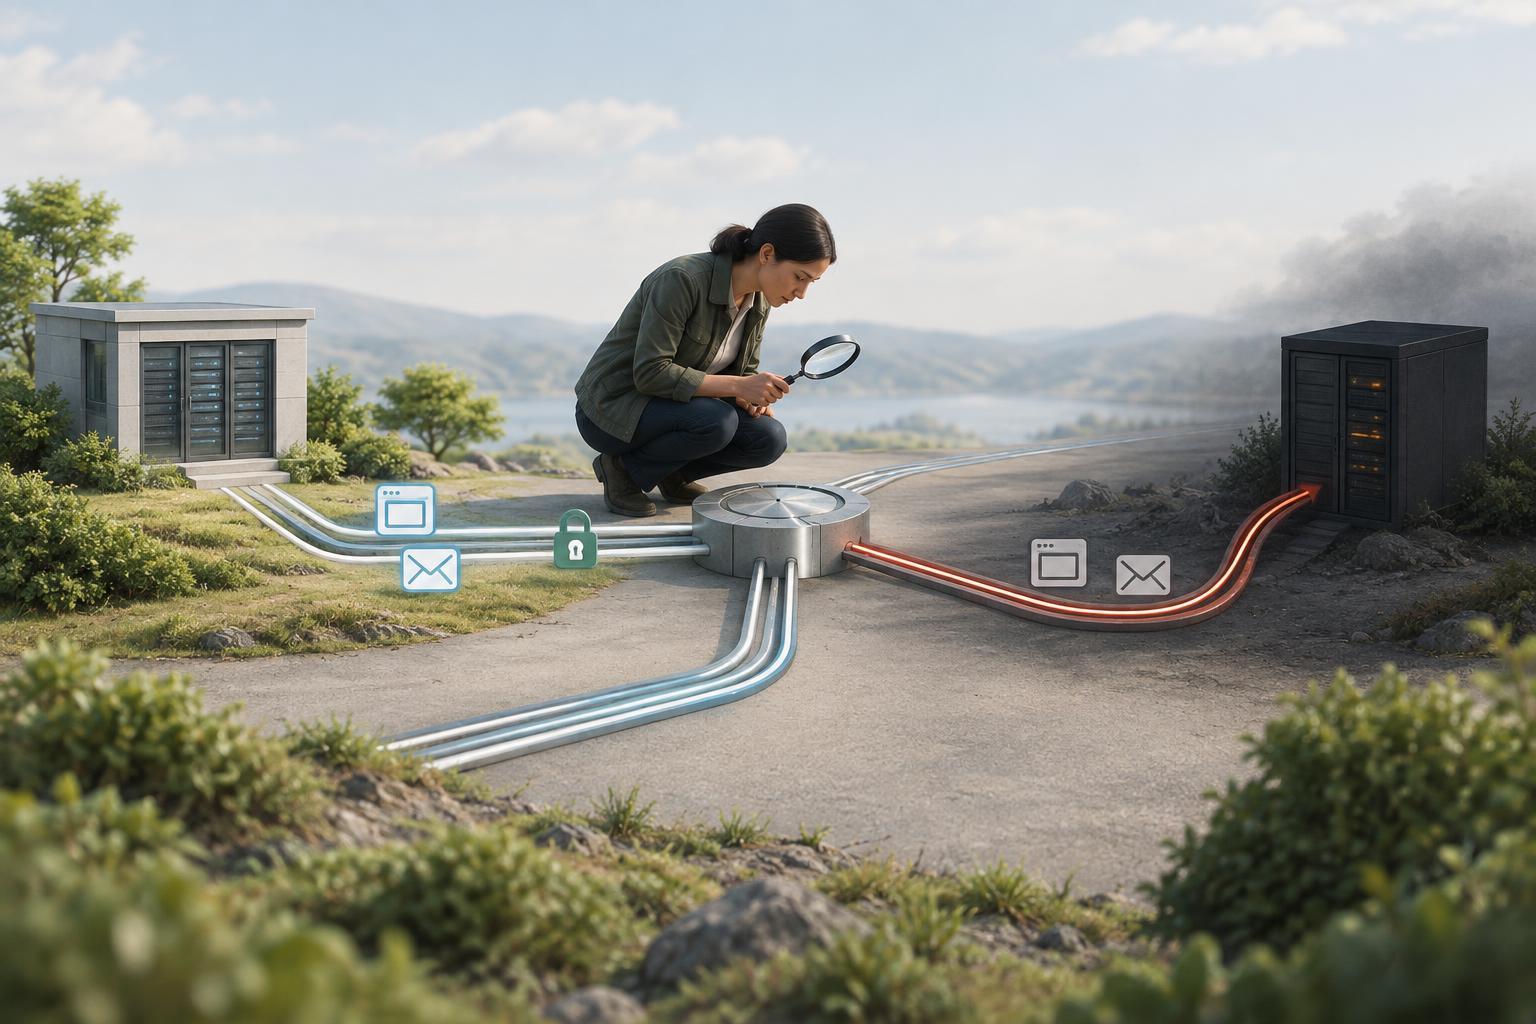
Why a nameserver change matters
Nameservers tell the DNS system where to look for a domain’s records. For most domains, the registrar account is where you choose the authoritative nameservers, and the parent zone publishes that delegation. If someone changes it without permission, queries may be directed to a different DNS provider. That provider could serve different website addresses, mail-routing records, or other answers, even if the records at your usual provider remain untouched.
This is distinct from changing a single record inside your existing DNS zone. A changed A record can affect a website; a changed MX record can affect mail delivery. A changed delegation can put the entire zone under another set of authoritative nameservers. The impact depends on what those servers publish and which answers resolvers have cached. An unfamiliar nameserver is therefore a reason to investigate, not proof by itself that an attack has occurred.
Signs worth checking
Start with deviations from a known-good configuration. Examples include a registrar notification you did not expect, nameservers at the parent zone that differ from your approved list, or DNS answers that suddenly point to unfamiliar services. A website showing unexpected content, mail failing to arrive, or email authentication records disappearing may also prompt a check. These symptoms have many possible causes, so avoid treating any one of them as a diagnosis.
Be especially careful after legitimate changes. Moving DNS providers, renewing a domain, changing registrars, or restoring an account can coincide with temporary differences between cached answers. Compare the observed nameservers with a record of what your team approved and when. If no such record exists, ask the people who manage the domain before making changes: replacing an unfamiliar but legitimate delegation can cause another outage.
How to verify the delegation
Check the nameserver setting in your registrar account by navigating there directly, rather than following a link in an alert email. Then compare it with the delegation reported by the domain’s parent zone using a DNS lookup tool you trust. The registrar interface shows what the account is configured to request; the parent-zone result shows what is being published for the domain. If they disagree, allow for processing time and ask the registrar to clarify the status. You do not need to share a password, recovery code, or account screenshot with a public troubleshooting forum.
Next, query each listed authoritative nameserver for a few expected records, such as the website address, MX records, and relevant TXT records. Compare the answers with your documented configuration. Responses from a general-purpose DNS resolver may lag because of caching, so they are useful for understanding what some visitors may see but are not the best sole test of current delegation. If the domain uses DNSSEC, also check whether its parent-zone DS record still matches the intended setup; a mismatch can make an otherwise correct-looking zone fail validation.
Responding to a suspected unauthorized change
If the delegation is not approved, preserve what you can first: note the observed nameservers, affected domain, approximate discovery time, and relevant account notifications. Capture DNS results without including private account details. Contact the registrar through its official support channel, report the suspected unauthorized change, and ask about account activity and recovery options. If you still control the account, review authorized users, recovery methods, and recent changes.
Restoring the approved nameservers is important, but it may not address how the change happened. Secure the registrar account with a new, unique password and multifactor authentication where available; review email-account security too, since email is often used for account recovery. Check for altered contact details, added users, and other domain settings. Coordinate with your DNS and email providers to verify that their zones and services remain under your control. If DNSSEC is enabled, plan any DS-record correction with the DNS provider so the restored delegation validates properly.
Reducing the chance of a repeat
Keep a small, access-controlled inventory of each domain’s registrar, approved nameservers, DNS provider, account owners, and DNSSEC status. Record planned changes and confirm the published delegation afterward. Limit registrar access to people who need it, remove unused accounts, enable available security notifications, and consider registrar locking features as an additional safeguard. A lock is not a substitute for protecting sign-in and recovery methods.
Periodically compare the published delegation with your inventory, especially for domains that rarely change. If you find a difference, verify it with the responsible team before trying to fix it. DNS caching means users may continue to see different answers for a time after a correction, so confirm recovery at the authoritative servers and monitor resolver results separately. The goal is a repeatable process: know the intended delegation, detect deviations, and respond without putting account secrets at further risk.


