Why a cached answer matters
When you enter a domain name, your device usually asks a recursive DNS resolver to find its records. The resolver may already have a recent answer in its cache. If not, it asks other DNS servers and stores the answer for a period set by its time to live, or TTL. Caching makes repeat lookups faster and reduces unnecessary queries.
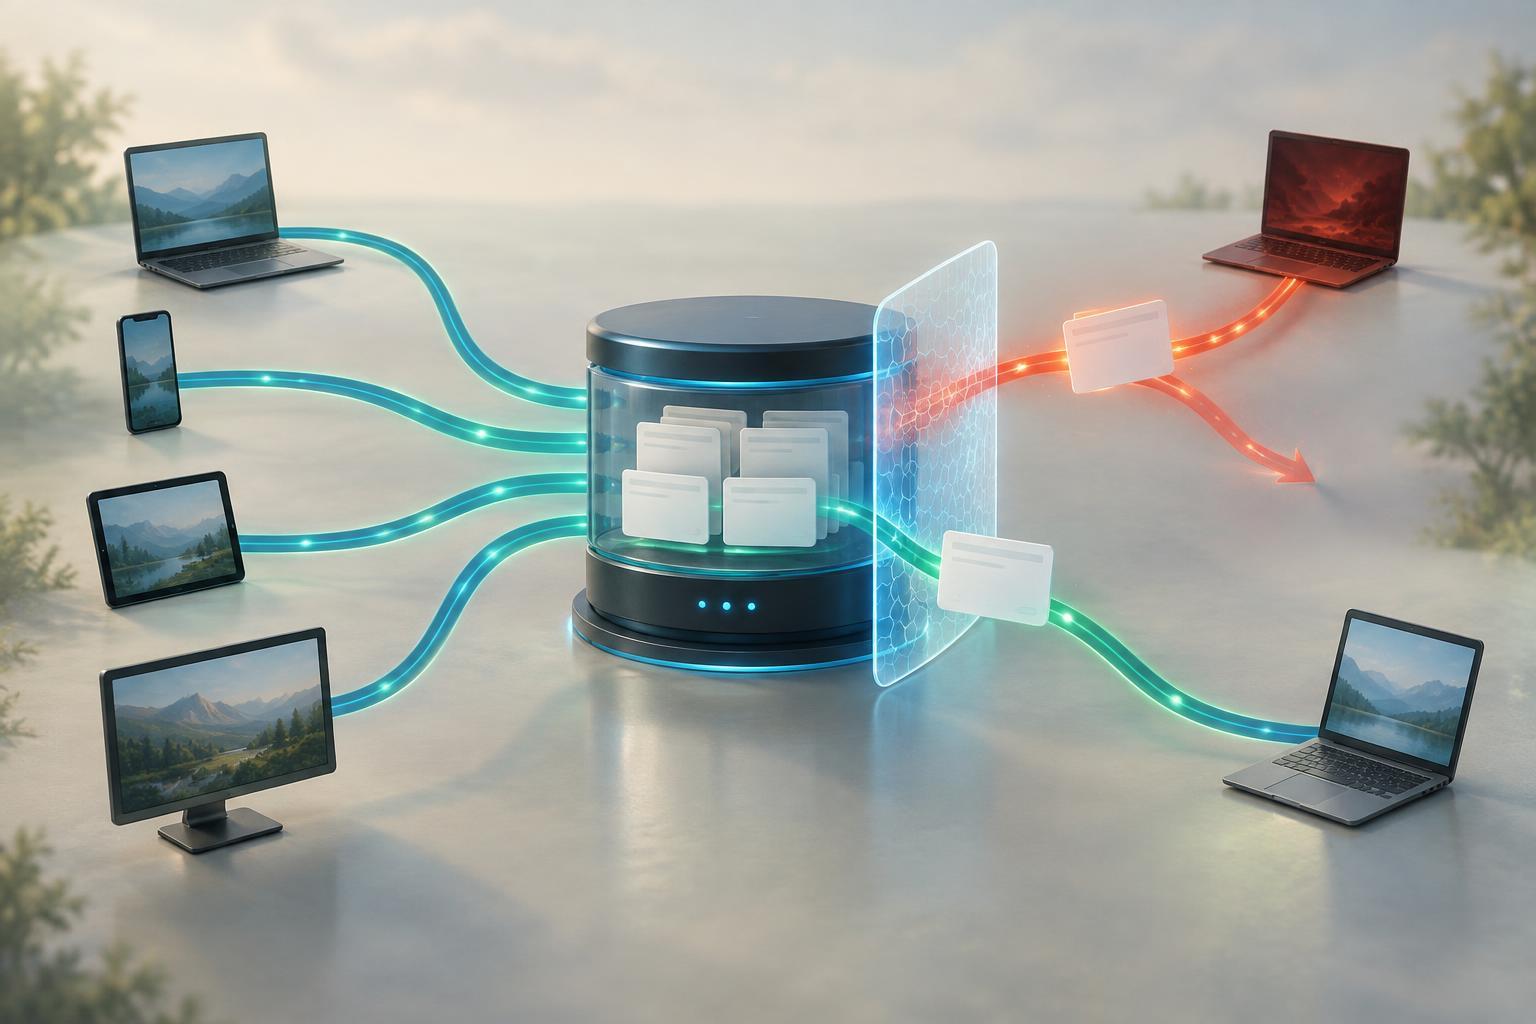
DNS cache poisoning means placing an incorrect DNS answer in that cache. For example, if a resolver caches a false address record for a website, people using that resolver may be directed to the wrong server until the entry expires or is removed. The effect depends on which record was changed and who relies on the affected resolver. Poisoning a shared resolver can affect multiple users; a false entry on one device may affect only that device.
How a forged answer can enter the cache
A common model is a race between a legitimate DNS response and a forged one. After the resolver sends a query, an attacker attempts to make a fake response appear to come from the server being asked. If the resolver accepts the forgery first and treats its contents as cacheable, it may store the false information. The attacker generally needs more than a plausible domain name: the response must match details of the outstanding query.
Historically, predictable query details made this easier. Resolvers now commonly vary values such as the query identifier and the network source port, making a blind forgery harder to match. A resolver should also check that a response corresponds to a query it actually made and came from the expected source. These checks reduce the chance of accepting an unsolicited answer, but they are not a guarantee against every attacker or network position.
Not every wrong DNS answer is cache poisoning. A mistaken record at an authoritative server, an altered hosts file, or a compromised router can also send someone to an unexpected destination. Distinguishing these causes matters because clearing a resolver’s cache will not fix an incorrect record published by the domain owner.
How resolvers limit what gets stored
Resolvers apply rules about which records in a response are relevant to the question and which server is allowed to supply them. These checks include bailiwick rules, which limit when a resolver accepts additional records accompanying an answer. Without such limits, a reply about one domain could try to smuggle in an address for an unrelated domain. Careful caching rules help prevent a response from becoming a source of authority over names it does not control.
Resolver software also needs timely maintenance. Implementations can have flaws even when the protocol-level checks are sound, so updates and conservative configuration remain important. TTLs bound how long ordinary cached entries are retained, but a short TTL is not a substitute for validating an answer before storing it. If a suspicious answer is already cached, a resolver operator may need to investigate and remove it rather than simply wait for expiration.
What DNSSEC adds—and what it does not
DNSSEC gives a validating resolver a way to check that supported DNS data is signed by the domain’s DNS operator and linked through a chain of trust. If a signed answer is replaced with a forged one that fails validation, the resolver should reject it rather than hand it to users as a valid answer. This provides a stronger check than relying only on whether a response appears to match a query.
DNSSEC coverage depends on both the domain’s configuration and the resolver performing validation. It does not validate unsigned domains, conceal DNS queries, or prove that the destination website itself is safe. A correctly signed record can still point to an unwanted destination if the domain’s authorized configuration is wrong or has been taken over. Website protections such as HTTPS address a different part of the connection and remain important.
A practical way to think about the risk
For a resolver operator, the useful priorities are to run maintained resolver software, avoid overly permissive caching behavior, use unpredictable query values, and enable DNSSEC validation where appropriate. Access controls also matter: a resolver intended only for a private network should not be left available to everyone on the internet.
For a site owner or user, an unexpected destination is a reason to check the whole path rather than assume cache poisoning. Compare results from trusted resolvers, inspect the domain’s authoritative records, and consider whether the problem is limited to one device or network. Do not enter credentials into a page that looks wrong while investigating. DNS cache poisoning is a specific failure of answer acceptance; understanding where the incorrect answer began is the first step toward correcting it.


